Security Operations Center Course in Pashan
 Boost Your IT Career with Hands-On SOC Training by SevenMentor
 Stay Ahead in the Digital Era with Advanced SOC Skills
 Learn Cloud Deployment, Management, and Automation from Expert Trainers

Start Today!
CONSULT WITH OUR ADVISORS
- Course & Curriculum Details
- Flexible Learning Options
- Affordable Learning
- Enrollment Process
- Career Guidance
- Internship Opportunities
- General Communication
- Certification Benefits
Request Call Back
Learning Curve for Security Operations Center in Pashan
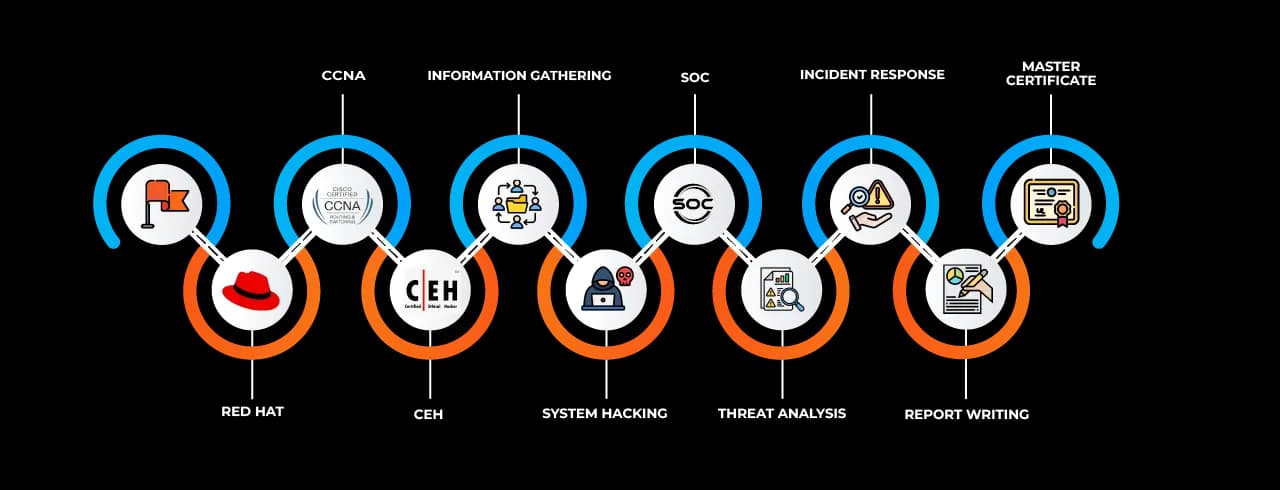
Master In Security Operations Center in Pashan Course
OneCourseMultipleRoles
Empower your career with in-demand data skills and open doors to top-tier opportunities.
Skills & Tools You'll Learn -
 OS ForensicsA forensic software that helps extract, search, and analyze system artifacts, logs, and file systems for investigation
 Kali LinuxA Debian-based penetration testing and ethical hacking operating system, pre-loaded with security tools.
 Wireshark A network protocol analyzer used for packet sniffing and traffic monitoring.
 NetworkMiner A network forensic analysis tool for extracting and analyzing packets.
 Hydra A fast brute-force password cracking tool for network authentication protocols.
 Splunk A security information and event management (SIEM) tool used for log analysis and threat detection.
 OSINT (Open-Source Intelligence)Collect publicly available data for cybersecurity investigations and threat analysis.
 VirusTotal Scan and analyze suspicious files, URLs, and domains for malware detection.
 Log AnalyzerProcess and analyze system logs to detect security incidents and unauthorized activities.
 Harvester Gather email addresses, subdomains, and public data for reconnaissance and OSINT.
 Google Dorks Use advanced search queries to uncover sensitive and exposed information online.
 Autopsy Perform digital forensics to recover and analyze deleted or hidden files.
 ModSecurity Implement a web application firewall (WAF) to protect against cyber threats.
 Socialphish Simulate phishing attacks to test and improve security awareness.
Why Choose SevenMentor Security Operations Center in Pashan
Empowering Careers with Industry-Ready Skills.

Specialized Pocket Friendly Programs as per your requirements

Live Projects With Hands-on Experience

Corporate Soft-skills & Personality Building Sessions

Digital Online, Classroom, Hybrid Batches

Interview Calls Assistance & Mock Sessions

1:1 Mentorship when required

Industry Experienced Trainers

Class Recordings for Missed Classes

1 Year FREE Repeat Option

Bonus Resources
Specialized Pocket Friendly Programs as per your requirements
Live Projects With Hands-on Experience
Corporate Soft-skills & Personality Building Sessions
Digital Online, Classroom, Hybrid Batches
Interview Calls Assistance & Mock Sessions
1:1 Mentorship when required
Industry Experienced Trainers
Class Recordings for Missed Classes
1 Year FREE Repeat Option
Bonus Resources

Fastest 1:1 doubt support

Flexible EMI Plans

Adaptive LMS

Free Wifi Facilities

Flexible Scheduling

Ongoing Career Support

Placement Drives

GitHub Project Implementations

Real World Topics

5/5 rating for 99% doubt Solutions

Be Different With Master Certificate

Latest Market Technology & Practical Training

Resume Building Session & Job Portals Training

Enhanced Capstone Projects for learning

Stand Out with an impressive Certificate

Weekday and Weekend Batches

Workshops & Seminars with Industry Experts

Unlimited Interview Calls

AWS Cloud Project Deployments

Live Quizzes

Resolve doubts any time through chat, voice notes, calling or meeting with instructors.
Curriculum For Security Operations Center in Pashan
BATCH SCHEDULE
Security Operations Center in Pashan Course
Find Your Perfect Training Session
Nov 8 - Nov 14
1 sessionNov 15 - Nov 21
2 sessionsNov 22 - Nov 28
1 sessionLearning Comes Alive Through Hands-On PROJECTS!
Comprehensive Training Programs Designed to Elevate Your Career
Create a SOC Environment
Implement Web Application on SOC Environment and Monitor It
Implement SIEM Environment
No active project selected.
Transform Your Future with Elite Certification
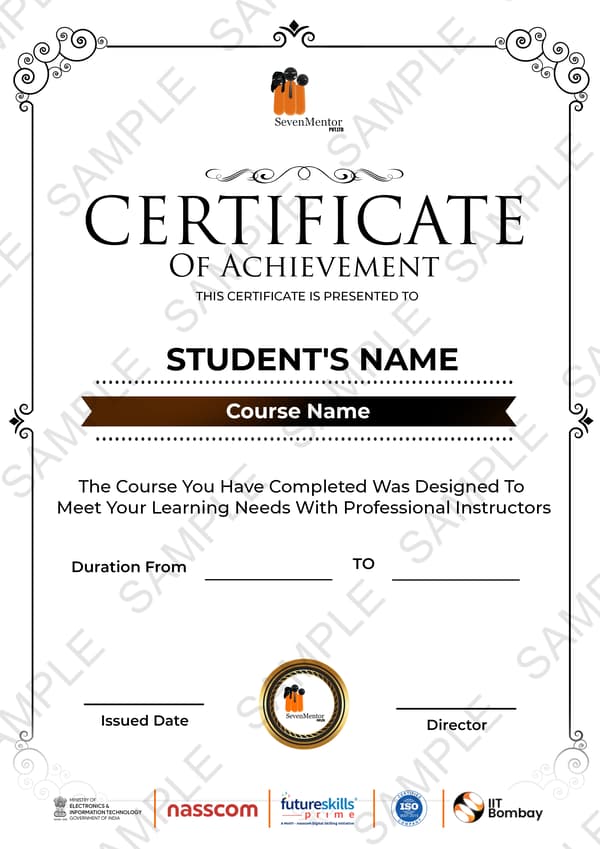
Add Our Training Certificate In Your LinkedIn Profile
Our industry-relevant certification equips you with essential skills required to succeed in a highly dynamic job market.
Join us and be part of over 50,000 successful certified graduates.


KEY Features that Makes Us Better and Best FIT For You
Expert Trainers
Industry professionals with extensive experience to guide your learning journey.
Comprehensive Curriculum
In-depth courses designed to meet current industry standards and trends.
Hands-on Training
Real-world projects and practical sessions to enhance learning outcomes.
Flexible Schedules
Options for weekday, weekend, and online batches to suit your convenience.
Industry-Recognized Certifications
Globally accepted credentials to boost your career prospects.
State-of-the-Art Infrastructure
Modern facilities and tools for an engaging learning experience.
100% Placement Assistance
Dedicated support to help you secure your dream job.
Affordable Fees
Quality training at competitive prices with flexible payment options.
Lifetime Access to Learning Materials
Revisit course content anytime for continuous learning.
Personalized Attention
Small batch sizes for individualized mentoring and guidance.
Diverse Course Offerings
A wide range of programs in IT, business, design, and more.
Course Content
Frequently Asked Questions
Everything you need to know about our revolutionary job platform
What topics are covered in the SOC Course?
Why choose SevenMentor Training for SOC training?
What tools and technologies will I learn in the SOC Course?
Does the SOC Certification include practical training?
How long is the SOC Course?
What career opportunities are available after completing the SOC training?
Does SevenMentor Institute in Pune offer placement support?
Is the SOC Course suitable for beginners?
What is the teaching methodology at SevenMentor Institute in Pune?
How does SOC Certification add value to my career?
Can I take SOC Classes online?
What makes SevenMentor the best institute for SOC training?
Will I receive study materials during the SOC Certification program?
Does the SOC Course cover advanced topics like threat intelligence and incident response?
How does SevenMentor Institute in Pune help with career growth after the course?
Invest In Your Future With Skills That Matter.
Investing in the right skills at the right place paves the way for long-term career success and growth. SevenMentor Institute equips you with industry-relevant expertise, ensuring you stay ahead in an evolving job market.
Career Support:
Beyond technical training, we provide comprehensive career assistance, including resume building, interview coaching, and job placement support.
Recognized Certification:
Earn globally recognized certifications that validate your expertise and enhance your employability.
Company Tie-Ups:
We collaborate with leading corporations, startups, and multinational companies to provide our students with exclusive job opportunities, internships, and industry exposure.
Take the first step to fast-track your future!