WAPT Training In Hinjewadi
 Master Web Application Penetration Testing with Industry Expert Trainers
 Learn Advanced Security Techniques to Identify and Exploit Web Vulnerabilities.
 Boost Your Cybersecurity Career with SevenMentor’s Hands-On WAPT Training.
Start Today!
CONSULT WITH OUR ADVISORS
- Course & Curriculum Details
- Flexible Learning Options
- Affordable Learning
- Enrollment Process
- Career Guidance
- Internship Opportunities
- General Communication
- Certification Benefits
Request Call Back
Learning Curve for Web Application Penetration Testing in Hinjewadi
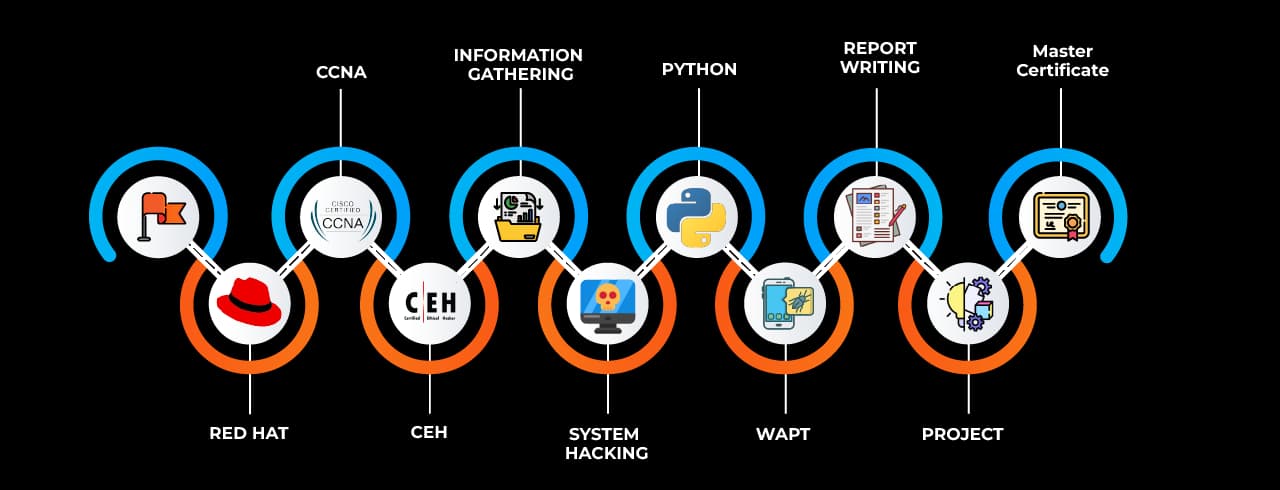
Master In Web Application Penetration Testing in Hinjewadi Course
OneCourseMultipleRoles
Empower your career with in-demand data skills and open doors to top-tier opportunities.
Skills & Tools You'll Learn -
 Nmap A network scanning tool used for discovering hosts and services on a network.
 Metasploit A widely used penetration testing framework for exploiting system vulnerabilities.
 Kali LinuxA Debian-based penetration testing and ethical hacking operating system, pre-loaded with security tools.
 Zenmap A graphical front-end for Nmap that simplifies network scanning and analysis.
 Wireshark A network protocol analyzer used for packet sniffing and traffic monitoring.
 Angry IP ScannerA fast and lightweight tool for scanning IP addresses and ports.
 Burp SuiteA web vulnerability scanner and penetration testing tool.
 Nessus A vulnerability scanner that helps identify security issues in systems and networks.
 Acunetix A web security scanner used to detect vulnerabilities like SQL injection and XSS.
 Social-Engineer Toolkit (SET) A tool for simulating social engineering attacks and phishing campaigns.
 Hydra A fast brute-force password cracking tool for network authentication protocols.
 Hashcat A password recovery tool used for cracking hashes with GPU acceleration.
 DVWA (Damn Vulnerable Web Application)A deliberately vulnerable web app for learning and testing web security.
 bWAPP (Buggy Web Application)A web application designed to practice and understand web vulnerabilities.
 Advanced Port ScannerA lightweight yet effective tool to scan and analyze open ports in a network.
 Gobuster A directory and subdomain brute-forcing tool used in web security assessments.
 FinalRecon A reconnaissance tool that gathers detailed information about web applications and domains.
Why Choose SevenMentor Web Application Penetration Testing in Hinjewadi
Empowering Careers with Industry-Ready Skills.

Specialized Pocket Friendly Programs as per your requirements

Live Projects With Hands-on Experience

Corporate Soft-skills & Personality Building Sessions

Digital Online, Classroom, Hybrid Batches

Interview Calls Assistance & Mock Sessions

1:1 Mentorship when required

Industry Experienced Trainers

Class Recordings for Missed Classes

1 Year FREE Repeat Option

Bonus Resources
Specialized Pocket Friendly Programs as per your requirements
Live Projects With Hands-on Experience
Corporate Soft-skills & Personality Building Sessions
Digital Online, Classroom, Hybrid Batches
Interview Calls Assistance & Mock Sessions
1:1 Mentorship when required
Industry Experienced Trainers
Class Recordings for Missed Classes
1 Year FREE Repeat Option
Bonus Resources

Fastest 1:1 doubt support

Flexible EMI Plans

Adaptive LMS

Free Wifi Facilities

Flexible Scheduling

Ongoing Career Support

Placement Drives

GitHub Project Implementations

Real World Topics

5/5 rating for 99% doubt Solutions

Be Different With Master Certificate

Latest Market Technology & Practical Training

Resume Building Session & Job Portals Training

Enhanced Capstone Projects for learning

Stand Out with an impressive Certificate

Weekday and Weekend Batches

Workshops & Seminars with Industry Experts

Unlimited Interview Calls

AWS Cloud Project Deployments

Live Quizzes

Resolve doubts any time through chat, voice notes, calling or meeting with instructors.
Curriculum For Web Application Penetration Testing in Hinjewadi
BATCH SCHEDULE
Web Application Penetration Testing in Hinjewadi Course
Find Your Perfect Training Session
Oct 4 - Oct 10
1 sessionOct 11 - Oct 17
2 sessionsOct 18 - Oct 24
1 sessionLearning Comes Alive Through Hands-On PROJECTS!
Comprehensive Training Programs Designed to Elevate Your Career
TryHackMe
Find a Vulnerability on a Website and Report It
Bug Hunting
VAPT (Vulnerability Assessment and Penetration Testing)
No active project selected.
Transform Your Future with Elite Certification
Add Our Training Certificate In Your LinkedIn Profile
Our industry-relevant certification equips you with essential skills required to succeed in a highly dynamic job market.
Join us and be part of over 50,000 successful certified graduates.


KEY Features that Makes Us Better and Best FIT For You
Expert Trainers
Industry professionals with extensive experience to guide your learning journey.
Comprehensive Curriculum
In-depth courses designed to meet current industry standards and trends.
Hands-on Training
Real-world projects and practical sessions to enhance learning outcomes.
Flexible Schedules
Options for weekday, weekend, and online batches to suit your convenience.
Industry-Recognized Certifications
Globally accepted credentials to boost your career prospects.
State-of-the-Art Infrastructure
Modern facilities and tools for an engaging learning experience.
100% Placement Assistance
Dedicated support to help you secure your dream job.
Affordable Fees
Quality training at competitive prices with flexible payment options.
Lifetime Access to Learning Materials
Revisit course content anytime for continuous learning.
Personalized Attention
Small batch sizes for individualized mentoring and guidance.
Diverse Course Offerings
A wide range of programs in IT, business, design, and more.
Course Content
Frequently Asked Questions
Everything you need to know about our revolutionary job platform
Do I Need a Cybersecurity Background for This Course?
Will This Course Teach How to Find and Exploit Web Vulnerabilities?
What Kind of Jobs Can I Get After This Course?
Does This Course Cover Security Tools Like Burp Suite and Metasploit?
Can Freelancers Also Benefit from This Course?
What’s the Best Way to Practice Web Penetration Testing After Training?
Is This Course Only for IT Professionals or Anyone Can Join?
What Topics Are Covered in Web Penetration Testing Training?
Do I Need to Know Programming for This Course?
Will I Get a Certification After Completing This Course?
How Long Does It Take to Complete the Training?
Can This Course Help Me Become a Bug Bounty Hunter?
How Is Web Penetration Testing Different From Network Security?
Is Cybersecurity a Good Career Option?
Does This Course Teach How to Bypass Firewalls and Security Protections?
Invest In Your Future With Skills That Matter.
Investing in the right skills at the right place paves the way for long-term career success and growth. SevenMentor Institute equips you with industry-relevant expertise, ensuring you stay ahead in an evolving job market.
Career Support:
Beyond technical training, we provide comprehensive career assistance, including resume building, interview coaching, and job placement support.
Recognized Certification:
Earn globally recognized certifications that validate your expertise and enhance your employability.
Company Tie-Ups:
We collaborate with leading corporations, startups, and multinational companies to provide our students with exclusive job opportunities, internships, and industry exposure.
Take the first step to fast-track your future!